News Articles
News Articles
IRAP explained with 6clicks
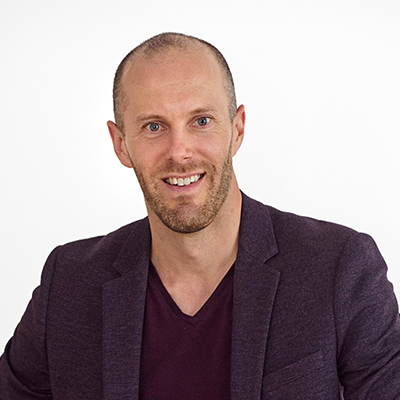
Andrew Robinson, co-founder of 6clicks
IRAP isn’t a badge. It isn’t a certificate. And it isn’t easy to achieve.
It’s an independent assessment framework used by the Australian Government to test whether systems handling sensitive data can be trusted.
IRAP – short for the Information Security Registered Assessors Program – is overseen by the Australian Signals Directorate (ASD) and creates a pool of ASD-endorsed assessors who can be used to assess systems against the Australian Government’s Information Security Manual (ISM).
Despite its importance, IRAP remains poorly understood outside cyber security circles. It’s also something relatively few commercial organisations undertake voluntarily, due to the scale, cost and complexities involved.
PharmacyID undertook its first IRAP assessment in 2023, working with IRAP assessor and cyber security expert Andrew Robinson, co-founder of 6clicks, a cyber governance, risk and compliance platform used extensively across government and critical infrastructure.
Andrew says that one of the most common misconceptions about IRAP is that it is a certification organisations can “hold”.
“IRAP itself isn’t a certificate in the same way you can be certified to ISO 27001,” Andrew explains.
“IRAP is a credential for people. It qualifies the assessors who are authorised to perform independent assessments against the Australian Government’s Information Security Manual.”
The ISM now contains more than 1,000 security controls spanning governance, personnel, physical security, cyber systems, encryption, access management and incident response. It is updated quarterly.
“The purpose of IRAP is to ensure the people conducting these assessments have the expertise to interpret and apply those controls properly,” Andrew says, “and to keep up with how quickly things change.”
Why government relies on IRAP
Government agencies can assess their own systems, but independent IRAP assessments become critical when services are delivered by third parties.
“If you’re a commercial organisation providing systems or services to government agencies, they need confidence that you’re protecting their information properly,” Andrew says.
IRAP assessments go well beyond surface-level checks. They include close technical scrutiny of systems – from encryption in transit and at rest, firewalls and network separation, to identity and access management, logging and monitoring, right down to physical cabling in some cases.
Beyond the technical detail, assessments also examine governance and process controls, including roles and responsibilities, incident response, third-party engagement and documentation.
That breadth is intentional.
“These systems often support critical services. If they’re disrupted, or their integrity is compromised, the consequences extend well beyond the organisation itself,” Andrew says.
Under the Information Security Manual, organisations are expected to undergo IRAP assessment every two years.
“That might sound infrequent given how fast technology changes,” Andrew says, “but IRAP assessments are resource-intensive. For large or complex environments, preparation alone can take years.”
Major system changes, such as moving data centres, introducing AI or making significant architectural shifts, can trigger reassessment sooner.
Despite being in place for around 20 years, IRAP assessments remain relatively rare.
“There’s been an increase in the number of IRAP assessors,” Andrew says, “but that doesn’t necessarily mean more organisations are undergoing assessment.”
He estimates only a small proportion of Australian businesses ever complete IRAP, typically those hosting government data or delivering outsourced systems on behalf of public sector agencies.
What IRAP signals to the market – and why it matters now
Beyond contractual requirements, Andrew says IRAP sends a strong signal about an organisation’s approach to security.
“For organisations like PharmacyID, identity is part of the security ecosystem,” he says. “If you’re providing services that help secure access to information, it makes sense to hold yourself to a very high standard.”
“Being able to demonstrate that you’ve undergone IRAP assessment, that the report exists and can be shared, builds confidence.”
With rapid advances in AI and increasing cyber threats, Andrew says governments are reasserting control over how and where information is processed.
“We’re seeing a focus on sovereignty – where data is stored, where systems are hosted, and who ultimately controls them,” he says.
“As technology accelerates, the need for strong, independent assurance frameworks like IRAP only increases.”
For organisations entrusted with sensitive data, that assurance can make all the difference.
In PharmacyID’s case, it means confidence that information handled through its document verification services, nationally coordinated criminal history checks and identity verification systems is secured within encrypted environments and assessed against some of the most rigorous cyber security controls in the country.